Recent Posts
Romance fraud cost Americans $1.14 billion in 2023 by the Federal Trade Commission’s count, with a median loss of $2,000 per victim, and the FBI’s Internet Crime Complaint Center logged another $652 million in confidence and romance losses the same year. Those numbers land hardest on the corner of the industry with the widest trust gap: international online dating, where two people in different countries, languages, and legal systems have to decide whether the person on the other end of the screen exists. The platforms that survive in that corner are the ones that treat verification as a product, and the engineering behind it looks a lot like what Michigan’s cybersecurity firms have been selling to banks for a decade.
This piece walks through the three layers that now separate a credible cross-border platform from a credit-draining one, the AI that sits under each, and where the gaps still are.
Why Cross-Border Platforms Attract the Worst Fraud
Domestic dating apps can lean on friction that international platforms cannot. A Tinder match in Grand Rapids can meet for coffee on Thursday, which ends most impersonation schemes within a week. A match between a Detroit engineer and a woman in Lviv or Bogotá may run for months before an in-person meeting, and the standard scam script exploits exactly that delay: build rapport, invent a crisis, ask for money, disappear. Deloitte’s financial services research group has projected that generative AI could push fraud losses in the United States to $40 billion by 2027, and deepfaked video calls are the fastest-growing piece of that forecast.
Add a language barrier and the problem compounds. A scammer working through translation software produces the same slightly stilted English as a real person working through translation software, which strips users of one of their oldest detection tools.
Layer One – Proving a Face Is Live
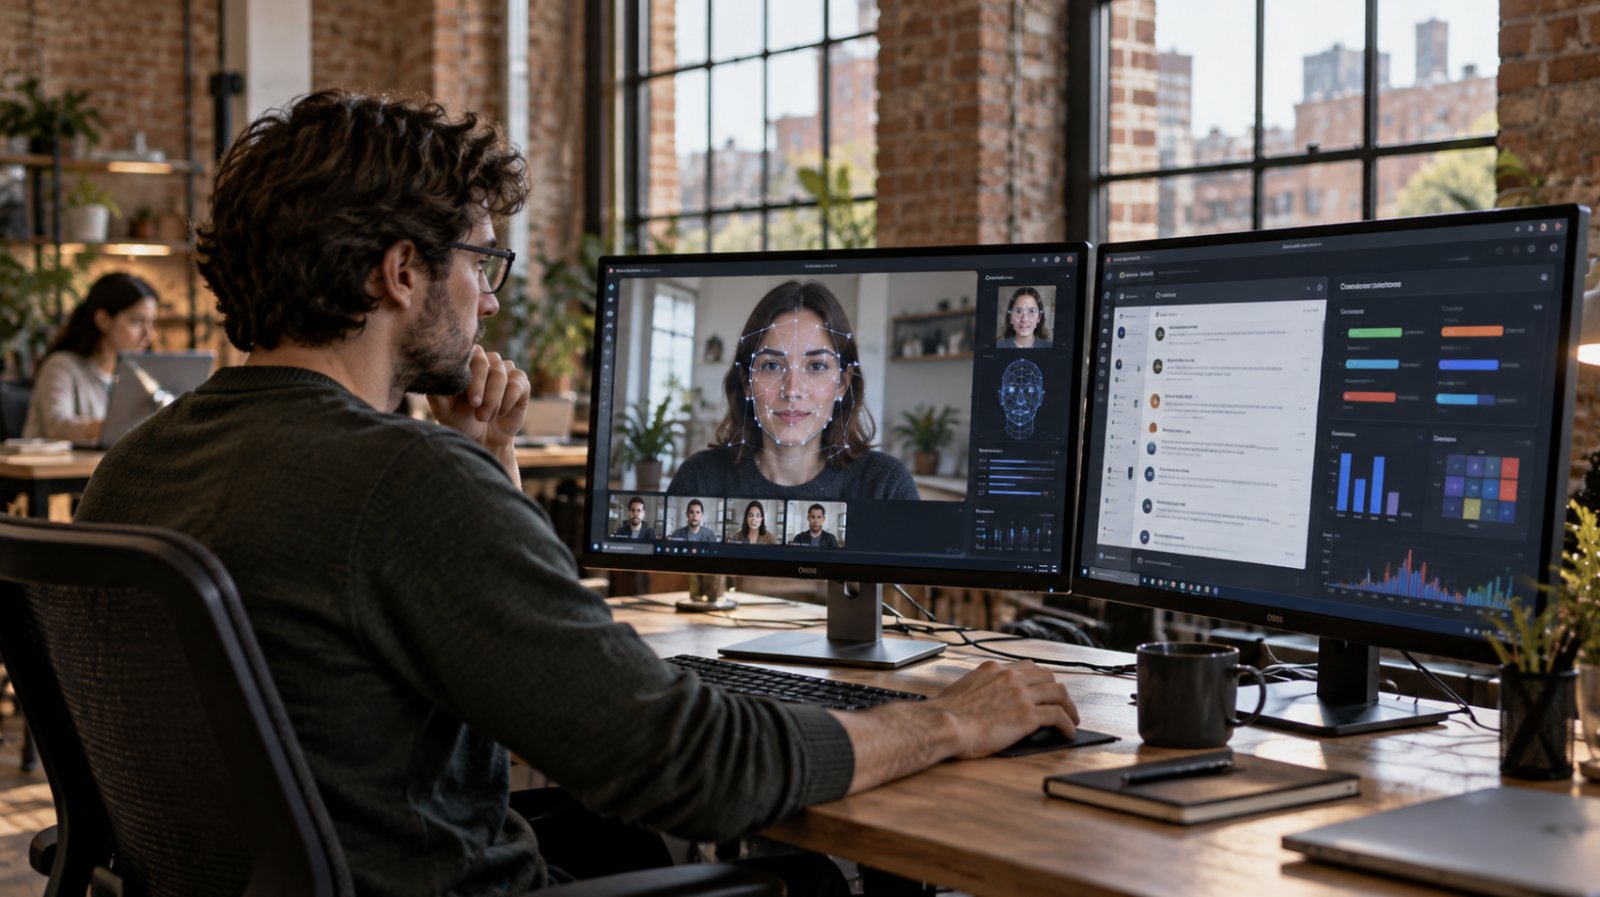
The first control is the video selfie. Tinder, Bumble, and Hinge all ask users to record a short clip following on-screen prompts, then match the frames against profile photos. The underlying standard is presentation attack detection under ISO 30107-3, the same liveness framework used in banking apps, and it screens out printed photos, replayed videos, and most current deepfakes by checking for depth, blink patterns, and how light moves across skin.
International platforms that operate through local partner agencies add a second version of the same idea: a staff member in the woman’s home city meets her in person, checks a passport, and records the verification on file. That is slower and more expensive than a selfie, roughly $10 to $25 per profile in staff time against $1 to $3 for an automated identity check, and it produces a verification an algorithm cannot spoof.
Layer Two – Proving the Face Has a Name
Liveness proves a human is present. It does not prove who. Government ID verification, which Tinder rolled out across the United States in 2024, matches the selfie to a driver’s license or passport through a third-party identity vendor. Marriage-oriented international platforms have a legal floor beneath that: the International Marriage Broker Regulation Act of 2005 requires them to collect an American client’s criminal and marital history and disclose it to the foreign user before contact begins.
| Trust layer | What it proves | What it still misses |
|---|---|---|
| Video selfie with liveness check | A live human recorded the clip | Who that human is |
| Government ID match | The face matches a real document | Intent; a verified person can still run a scam |
| In-person agency verification | Identity and physical presence in a stated city | Depends on the agency’s own honesty and audits |
| AI message classifiers | Scam scripts, money requests, off-platform redirects | Slow-burn manipulation that never trips a keyword |
| Payment controls | Blocks transfers between users inside the app | Requests moved to WhatsApp or crypto |
The table’s right-hand column explains why no single vendor sells a complete answer. Each layer closes one hole and opens a view of the next one.
Layer Three – Catching the Script in the Messages
The most measurable gains in the past two years came from language models reading conversations. Bumble’s Deception Detector, launched in February 2024, uses a machine-learning model to score profile authenticity and message patterns; in testing it blocked 95 percent of flagged spam and scam accounts automatically, and user reports of fake profiles fell 45 percent within two months. Tinder’s earlier prompts, which flag a message as potentially harmful before it is sent, work on the same principle in the other direction.
For cross-border platforms, the classifiers have to work in two languages at once, and the tell-tale patterns differ. A request for a $300 “visa fee” reads differently in Ukrainian than in Spanish, so the training data has to be built per market. Platforms that run real-time AI translation inside the chat, which several now do, get a bonus: the translation layer sees every message in a normalized form, which makes scam-pattern detection easier than on apps where users paste text from outside tools. There is a useful roundup of AI translation tools in international dating that shows how far that layer has come since the copy-and-paste era.
Matchmaking Is the Part Nobody Audits
Verification gets the headlines, while matching gets the revenue. Hinge’s “Most Compatible” feature runs on the Gale-Shapley algorithm, the stable-matching method that earned Lloyd Shapley a share of the 2012 Nobel Prize in economics, and it pairs users by who is likely to reciprocate, with raw profile scores treated as secondary. Cross-border platforms use simpler collaborative-filtering models, and the incentive problem is obvious: a platform paid per message has no reason to surface the one match who would end your subscription.
What surprised me, reading the vendor documentation, was how few platforms publish any matching metrics at all. Verification rates, yes. Fraud takedowns, sometimes. Conversion from match to in-person meeting, almost never. That silence is where a Michigan startup could make its name.
What Michigan Founders Could Build
Ann Arbor already produced one identity company that changed an industry: Duo Security, founded in 2010 and sold to Cisco in 2018 for $2.35 billion, made two-factor authentication ordinary for enterprise logins. The dating industry needs the equivalent for cross-border trust, and the gaps are specific.
- Deepfake detection tuned for low-bandwidth video calls, where compression hides the artifacts current models rely on.
- Portable verification: an identity check completed on one platform that a user can carry to another.
- Bilingual scam classifiers trained on Ukrainian, Polish, Spanish, and Tagalog conversation data.
- Escrow-style payment rails for legitimate cross-border expenses like translated documents and flights.
- Audited matching metrics that a consumer can compare across platforms.
Each of those is a security problem before it is a dating problem, which puts it squarely in the wheelhouse of the state’s cyber ecosystem: Merit Network’s cyber range, the University of Michigan and Michigan State security labs, and the automotive suppliers who have spent a decade on in-vehicle authentication. The market is global, the incumbents are slow, and the fraud numbers are growing faster than the user base. A verification stack that works for a bride in Kharkiv and a groom in Kalamazoo will work for a lot of other things too.
